
Static Analysis
Static analysis allows you to examine files and code without execution, uncovering threats safely and efficiently.
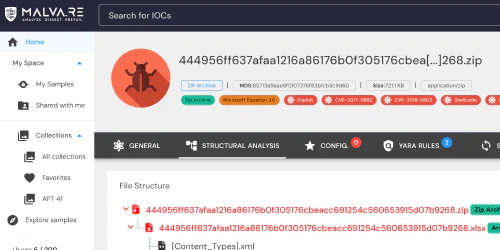
A reverse engineer's reading of DarkCloud 4.9: understanding the VB6 runtime, following the data collection and telling active transports apart thanks to the code reconstructed with VBReFormer Gen 2 (7.x).
Malware Research
A technical walkthrough of the UPX format and of how Malva.RE detects, decompresses and rebuilds UPX-packed PE files (NRV2B/D/E, LZMA, call/jump filters, imports, relocations, resources) without execution, emulation or sandbox, so the real payload reaches YARA, configuration extractors and family detection.
Malware Research Team
As of August 2025, Malva.RE provides deep static reports directly integrated into MalwareBazaar. This partnership highlights the resilience of our lightweight, execution-free malware analysis engine.
Malware Research Team
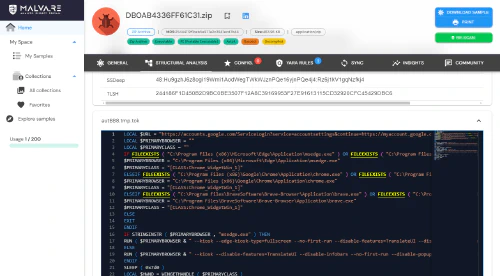
Malva.RE now supports AutoIt executable detection and decompilation, providing deep insights into complex malware attack chains with no execution risk.
Malva.RE Team
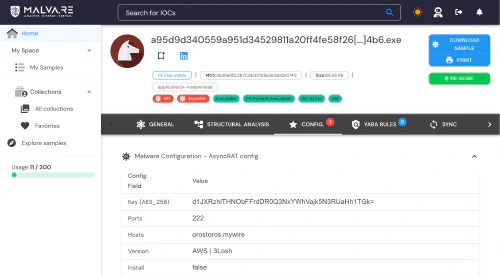
Extract configurations like C2 servers, encryption keys, and more from various malware families with Malva.RE’s unique static analysis approach.
Malva.RE Team
Discover Malva.RE, Yneos' groundbreaking malware analysis platform, blending state-of-the-art static analysis with AI for unparalleled efficiency and precision in detecting and analyzing cybersecurity threats.
Malva.RE Team