
Malware Configuration
Learn how to extract and analyze malware configurations to understand its functionality and intended targets.
DarkCloud 4.9 Decompiled with VBReFormer Gen 2 (7.x)
A reverse engineer's reading of DarkCloud 4.9: understanding the VB6 runtime, following the data collection and telling active transports apart thanks to the code reconstructed with VBReFormer Gen 2 (7.x).
Tags:
DarkCloud, VBReFormer, VBReFormer Gen 2, Visual Basic 6, VB5, VB6, YARA, Static Analysis, Malware Configuration
Malware Research
Malware Research
25 min read
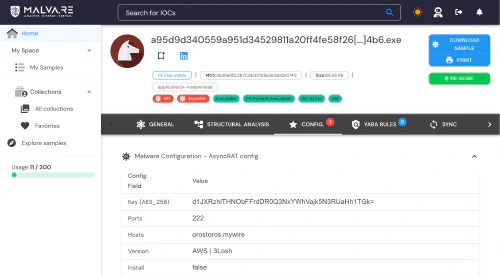
Malware Configuration Extraction
Extract configurations like C2 servers, encryption keys, and more from various malware families with Malva.RE’s unique static analysis approach.
Malva.RE Team
Malva.RE Team
5 min read