
Decompilation
Decompilation - Explore our articles.
Malva.RE Decompiles VB5/VB6 with VBReFormer Gen 2
What support for Visual Basic 5/6 executables changes in a Malva.RE report: sources reconstructed with VBReFormer Gen 2 (7.x), browsable procedure by procedure, and, for DarkCloud, an exfiltration configuration read in the code rather than guessed from strings. The DarkCloud 4.9 case serves as the example.
Malware Research
Malware Research
6 min read
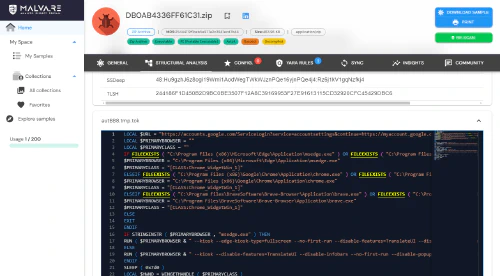
Advanced AutoIt Executable Decompilation with Malva.RE
Malva.RE now supports AutoIt executable detection and decompilation, providing deep insights into complex malware attack chains with no execution risk.
Malva.RE Team
Malva.RE Team
3 min read