
Features
Features - Explore our articles.
What support for Visual Basic 5/6 executables changes in a Malva.RE report: sources reconstructed with VBReFormer Gen 2 (7.x), browsable procedure by procedure, and, for DarkCloud, an exfiltration configuration read in the code rather than guessed from strings. The DarkCloud 4.9 case serves as the example.
Malware Research
A technical walkthrough of the UPX format and of how Malva.RE detects, decompresses and rebuilds UPX-packed PE files (NRV2B/D/E, LZMA, call/jump filters, imports, relocations, resources) without execution, emulation or sandbox, so the real payload reaches YARA, configuration extractors and family detection.
Malware Research Team
Malva.RE now supports AutoIt executable detection and decompilation, providing deep insights into complex malware attack chains with no execution risk.
Malva.RE Team
Learn about the advanced techniques of VBA Stomping and VBA Purging, and discover how Malva.RE, powered by vbaDNA technology, offers the most effective solution for detecting and analyzing these sophisticated threats hidden within Microsoft Office macros.
Malva.RE Team
Extract configurations like C2 servers, encryption keys, and more from various malware families with Malva.RE’s unique static analysis approach.
Malva.RE Team
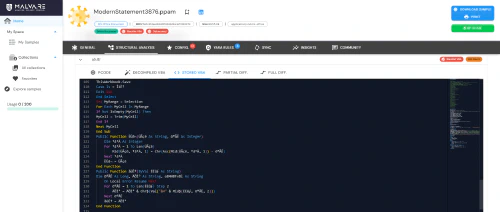
Accurate VBA decompilation and advanced detection of obfuscation techniques like VBA stomping and purging, all fully integrated into Malva.RE's automated analysis workflow.
Malva.RE Team
Discover how Malva.RE analyzes multi-level malware efficiently through fast structural dissection, with no execution, designed for SOC, CERT and malware research teams.
Malva.RE Team